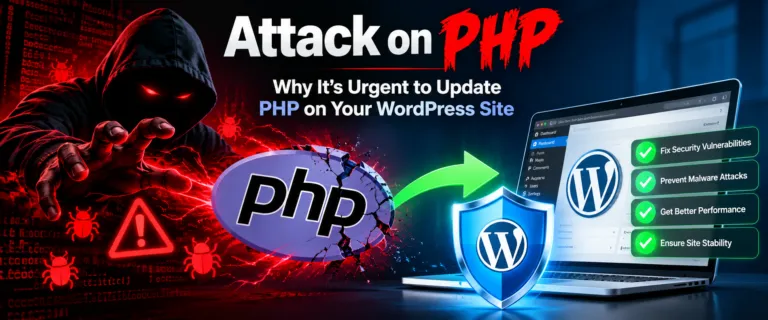
If your website, patient portal or online store runs on PHP, this week’s security news is about you. Two critical flaws in the PHP engine itself, tracked as CVE-2026-109618 and CVE-2026-109619 and nicknamed the PHP2Shell vulnerability, can let an attacker run commands on a server using nothing more than specially crafted web requests. No login is needed.
The good news is that patches exist and, so far, researchers haven’t confirmed any successful real-world break-ins. The less good news is that scanning is already enormous, a working bypass for a key defense has been shown, and a huge number of servers haven’t been updated. Here’s what happened, who’s at risk, and what to do about it.
Key Takeaways
- PHP2Shell is a pair of critical flaws (CVSS 9.2) in PHP core that allow unauthenticated remote code execution. Fixes shipped in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
- Attackers are scanning at massive scale and trying to install Mirai-style botnet malware, but researchers have reported no confirmed successful compromises yet.
- Because the bug is in PHP itself, even a WordPress, Drupal or Joomla site with clean code is exposed if the server’s PHP version is vulnerable.
- Sites on PHP 8.1 or older need to move to a supported version or confirm their host has backported the fix.
- This week’s job: find your PHP version, update, then confirm it with whoever hosts or manages your site.
What Is the PHP2Shell Vulnerability?
PHP2Shell is the name given to two vulnerabilities in the core of the PHP language, the engine behind a large share of the web, including WordPress. Both carry a severity score of 9.2 out of 10, and together they can lead to unauthenticated remote code execution (RCE). In plain terms: a stranger on the internet could make your server run their commands.
PHP published emergency patches on October 21, 2026. According to The Hacker News, the fixes are in PHP versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
Security firm Sysdig points out an important detail: the vulnerable code goes back to PHP 5.4, released in 2012, and the problem sits in the PHP engine rather than in any application. That’s the part many site owners miss. You can have a well-maintained WordPress site with no bad plugins and still be exposed, because the weakness is underneath it.
How Are Attackers Using It?
Within hours of the announcement, the internet lit up. Cloudflare reported tens of thousands of exploit attempts within 45 minutes of disclosure, hundreds of thousands within two hours, and millions by early October 22 (as relayed by The Hacker News).
Most of that traffic is noise from scanners and copy-paste attempts. Cisco Talos described the activity as mostly scanning plus uncoordinated payload attempts, which is typical when a public proof of concept appears before attackers have built their own tooling.
Still, a few details show where this is heading:
- Botnet recruitment. Some attempts aimed to enlist servers into a Mirai-derived botnet called Potassium. Sophos analyzed a sample and found a larger, updated version of a botnet first seen earlier in 2026, with downloader and network-disruption features. Botnets like this are mainly used to launch denial-of-service floods.
- Prepared tooling. SOCRadar found a ready-made exploit script on an attacker-controlled server, plus screening tools that checked about 20 websites for the right PHP version and settings. Hunt.io says the same operator targeted 123 servers, around 57 of them running PHP, many on unsupported 5.x to 7.x versions. None were exploited.
- A defense that can be beaten. VulnCheck demonstrated a technique that chains the two flaws, using a memory leak to get around ASLR, a protection that randomizes where code sits in memory. It works on x86-64 servers even with PHP’s recommended production error settings. That matters because ASLR was one of the main things standing between these bugs and reliable exploitation.
Is Anyone Actually Being Hacked?
Researchers at Previdian, Wordfence, Beelzebub and Dataminr all report the same pattern: plenty of probing, fingerprinting and attempts to confirm command execution, but no confirmed successful compromises so far. Sophos read the lack of results as a sign that attackers are struggling to build reliable exploits.
Don’t read that as a reason to wait. The VulnCheck work shows the technical barrier can be crossed, and the defensive window is the time between “patch available” and “reliable exploit widely used.” That window is open right now, and it won’t stay open.
The precautionary response has already been dramatic. Government, school and hospital sites across Asia, Europe and North America went offline while teams applied updates. The U.K. government confirmed 32 digital services were unavailable and four partly unavailable, and its National Cyber Security Centre sent roughly 50,000 warnings to organizations.
How Big Is the Exposure?
The numbers explain why people are comparing this to Log4Shell, a flaw that kept getting exploited long after it was fixed:
| Measure | Figure | Source |
|---|---|---|
| Hosts running PHP | 4.18 million | Censys |
| Web properties running PHP | 67.5 million | Censys |
| PHP services assessed as still vulnerable (Oct 23, 2026) | 34.4 million | Censys |
| Hosts on a supported PHP branch (8.2 to 8.5) | About 272,000 | VirusTotal estimate |
Figures as reported by The Hacker News on October 23, 2026. Censys revised its counts after improving its detection logic, so expect these to shift.
The long tail comes from older versions. Fixes aren’t available for older PHP releases, and Dataminr expects many organizations to stay vulnerable far longer than a simple patch cycle would suggest, because applications and appliances depend on their vendors to ship updates.
Which versions need what? Here’s the summary:
| Your PHP branch | What to do |
|---|---|
| 8.5 | Update to 8.5.12 or later |
| 8.4 | Update to 8.4.27 or later |
| 8.3 | Update to 8.3.36 or later |
| 8.2 | Update to 8.2.35 or later |
| 8.1, 8.0, 7.4 and older | Move to a supported branch, or confirm your operating system vendor has issued a backported fix |
What Should You Do This Week?
You don’t need to be a developer to handle the first steps. Work through these in order. If you’d rather hand this off, our guide to what managed IT services cover explains what a provider takes off your plate.
1. Find out what PHP version you’re running
Check your hosting control panel, ask your host, or ask whoever built your site. If you use WordPress, the Site Health screen shows the server’s PHP version. If nobody can tell you, that’s your first finding.
2. Update to a patched release
Move to one of the patched versions above. If you’re on 8.1 or older, this is also your push to upgrade properly rather than patching in place. Test first on a staging copy if you can, since PHP upgrades occasionally break older plugins and themes.
3. Ask your host in writing
On shared or managed hosting, the host controls the PHP version. Ask them to confirm the patched version is live for your account and whether they’ve applied any interim protections. PHP’s own announcement, linked in the sources below, lists the official guidance.
4. Add filtering as a second layer, not a substitute
A web application firewall or CDN can absorb a lot of the scanning noise. In Hunt.io’s data, ten of the targeted servers rejected the malicious request outright, including three of five behind Cloudflare. That’s encouraging, but filtering rules lag behind new exploit techniques, so treat it as a bonus on top of patching.
5. Look for signs of trouble
Review server and access logs from October 21 onward for strange requests, unexpected new files (especially PHP files in upload or session folders), unfamiliar admin users and unusual outbound connections. If you find anything, don’t clean it up quietly. Preserve the logs and bring in help.
6. Rotate secrets if you can’t rule out a compromise
VulnCheck notes that code running through this flaw would have the same access as your web application, which can include API keys, database credentials and internal services. If there’s any chance of exposure, change those credentials after the server is patched, not before.
7. Check your backups
Make sure you have a recent, clean backup that’s stored separately from the server. It’s the fastest way back if something goes wrong.
If you’d like a second set of eyes on steps 1 to 5, the free IT readiness self-assessment from panaTECH is a quick way to see where your gaps are.
Why Healthcare and Service Businesses Should Pay Extra Attention
Plenty of practices don’t realize how much of their daily operation rides on PHP. Patient portals, appointment-booking plugins, intake forms and the marketing website itself often run on it, usually installed by a vendor years ago and rarely looked at since. If your records system is web-based, our explainer on how EHR software works and connects to billing shows how many moving parts depend on that stack.
When a site like that goes down or gets compromised, the damage isn’t just technical. Appointment requests stop, forms collecting patient information may need to be taken offline, and billing and claims work slows when systems are unavailable. A steady revenue cycle management process depends on the systems around it staying up. For the billing pitfalls that get worse during outages, see our rundown of the top medical billing challenges for US providers.
Healthcare organizations also carry privacy obligations that make an incident more expensive than it would be for a brochure site. That’s one reason many practices lean on managed IT services for healthcare, where patching, monitoring and security are handled on a schedule rather than whenever someone remembers. Our overview of how IT improves care and efficiency in clinics shows what that looks like day to day.
The same applies to other businesses with customer-facing sites. Hotels and hospitality companies, for example, run booking engines and guest portals that can’t afford surprise downtime; our guide to managed IT services for hotels and hospitality covers what that support looks like.
The Search and Reputation Side of a Compromised Site
A hacked website hurts more than uptime. Injected spam pages, hidden redirects and malware warnings can drag down your search visibility and trust long after the code is cleaned up. If Google flags your site, recovery takes work.
It’s worth reading our breakdown of the Google June 2026 spam update to see how search engines treat spammy or compromised content. If you need help rebuilding on a clean, current stack, panaCLICKS offers website development, and its SEO team can help recover rankings after an incident.
Why This Won’t Be the Last Wake-Up Call
PHP2Shell isn’t a one-off. The Hacker News also reported that PHP warned of another unpatched RCE risk, tracked as CVE-2026-115560, just two days after the emergency patches. Details were still developing at the time of writing, so check PHP’s security announcements again before you consider the job finished. For the bigger picture, read what cyber security means for businesses and our piece on how AI-powered attacks are changing the threat landscape.
The deeper lesson is about process. Businesses that get hurt by headlines like this one usually have the same gap: nobody owns patching. Our look at future trends in managed IT for 2026 explains why security, cloud and compliance are increasingly bundled into one ongoing service, and panaTECH’s guide on reducing cybersecurity risk without building an in-house security team is a practical starting point if you’re a small team. Not sure whether you need outside help? Check the 10 signs your business needs managed cybersecurity services, or compare an in-house IT team with outsourced managed IT services.
Frequently Asked Questions
The PHP2Shell vulnerability is the nickname for two critical vulnerabilities in PHP core, CVE-2026-109618 and CVE-2026-109619, that can allow unauthenticated remote code execution through crafted HTTP requests. Both are scored 9.2 out of 10.
Fixes were released in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP 8.1, 8.0, 7.4 and older branches should be moved to a supported release, or covered by a backport from your operating system vendor.
It can be. The flaw is in the PHP engine, not in WordPress, so a site with clean WordPress code is still exposed if the server runs a vulnerable PHP version. Check the PHP version shown in WordPress Site Health and update through your host.
As of the reports published around October 23, 2026, several security firms said they’d seen heavy scanning and exploit attempts but no confirmed successful remote code execution. Researchers have, however, shown a working method to bypass ASLR, so the situation could change quickly.
Patching closes the known holes and is the single most important step. If your server was reachable before you updated, review logs for suspicious activity and rotate credentials if you can’t rule out a compromise.
Need Help Checking Your Exposure?
If you’re not sure what PHP version your site runs, or you’d rather hand patching and monitoring to a team that does it every day, book a discovery call with panaTECH. We’ll check your exposure, patch what needs patching, and set up the monitoring that keeps the next advisory from becoming an emergency.
About the Author